Snyk
Developer security scanner for code, dependencies, containers and AI-built apps
Launched 55 months agosnyk.io
Do you work on Snyk?
This listing is unclaimed. Claim it for free to edit the details, add screenshots and reply to reviews.
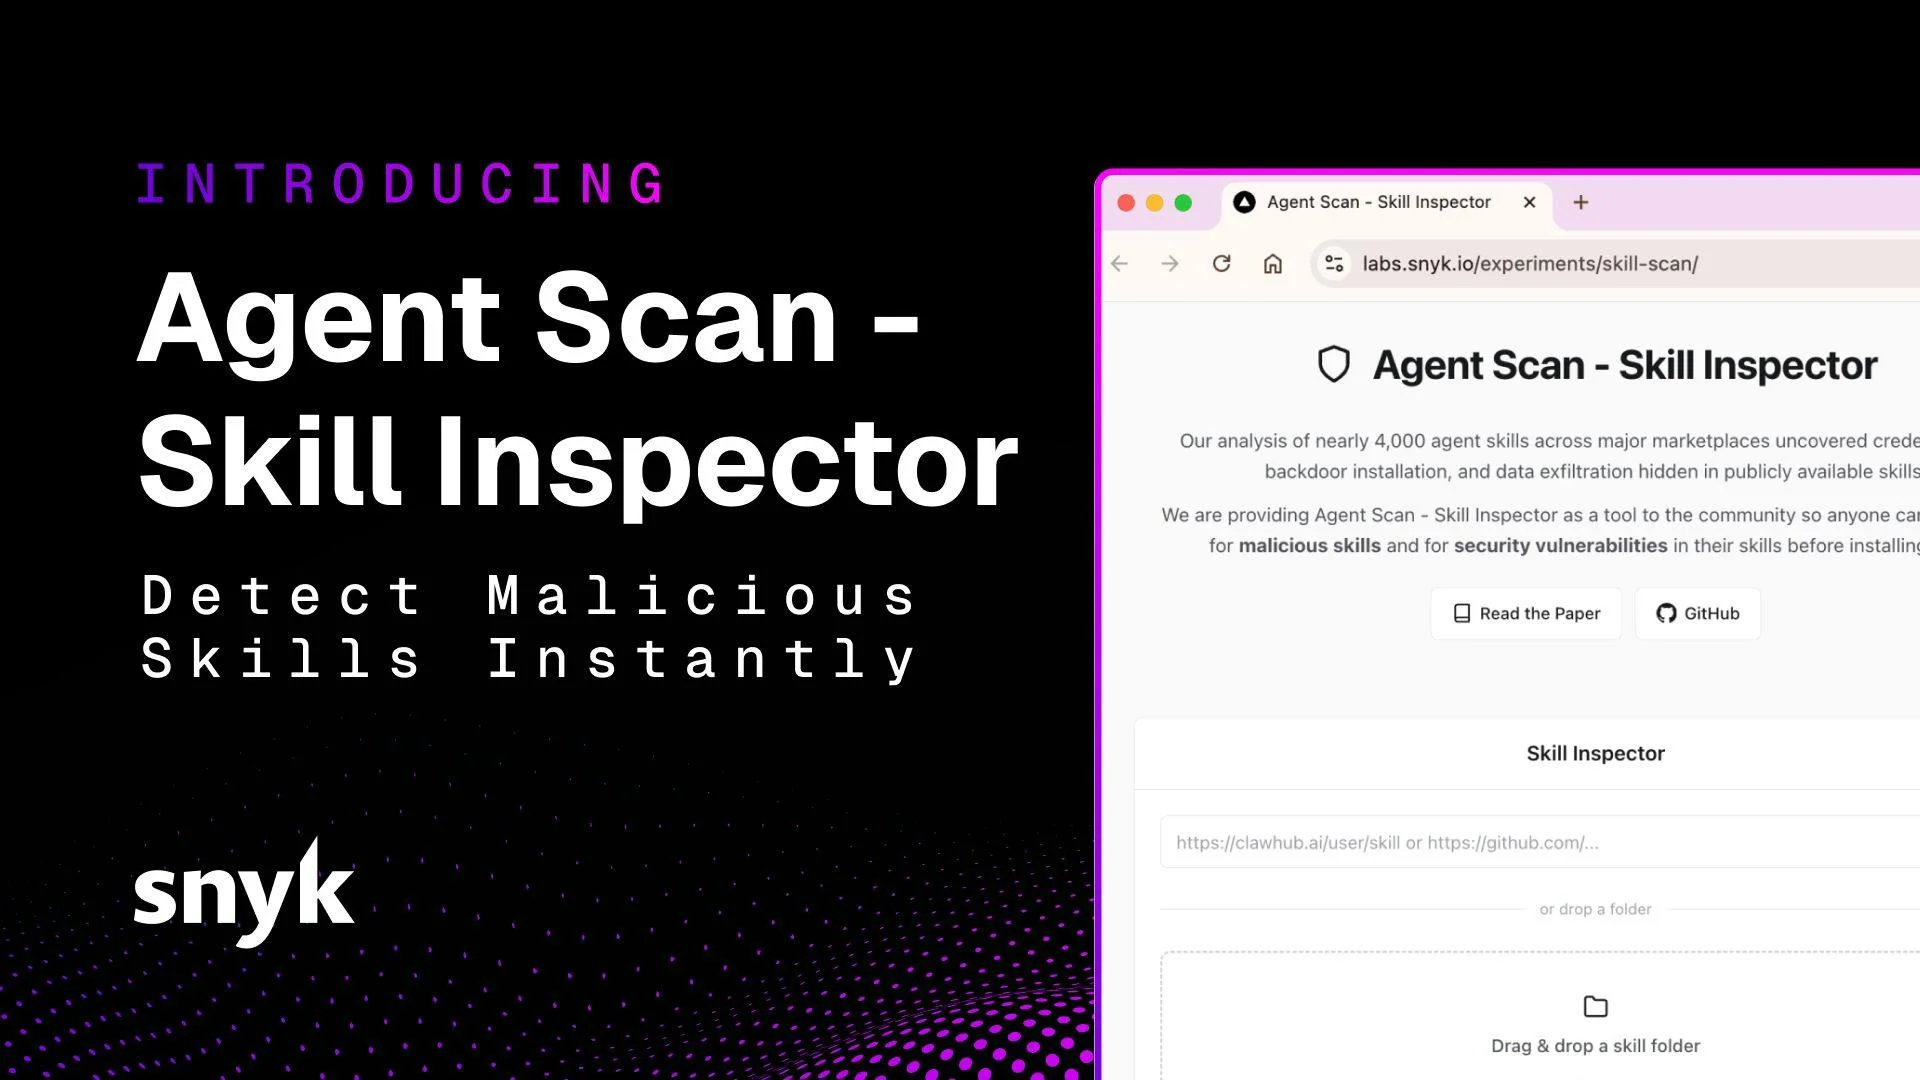 1 / 3
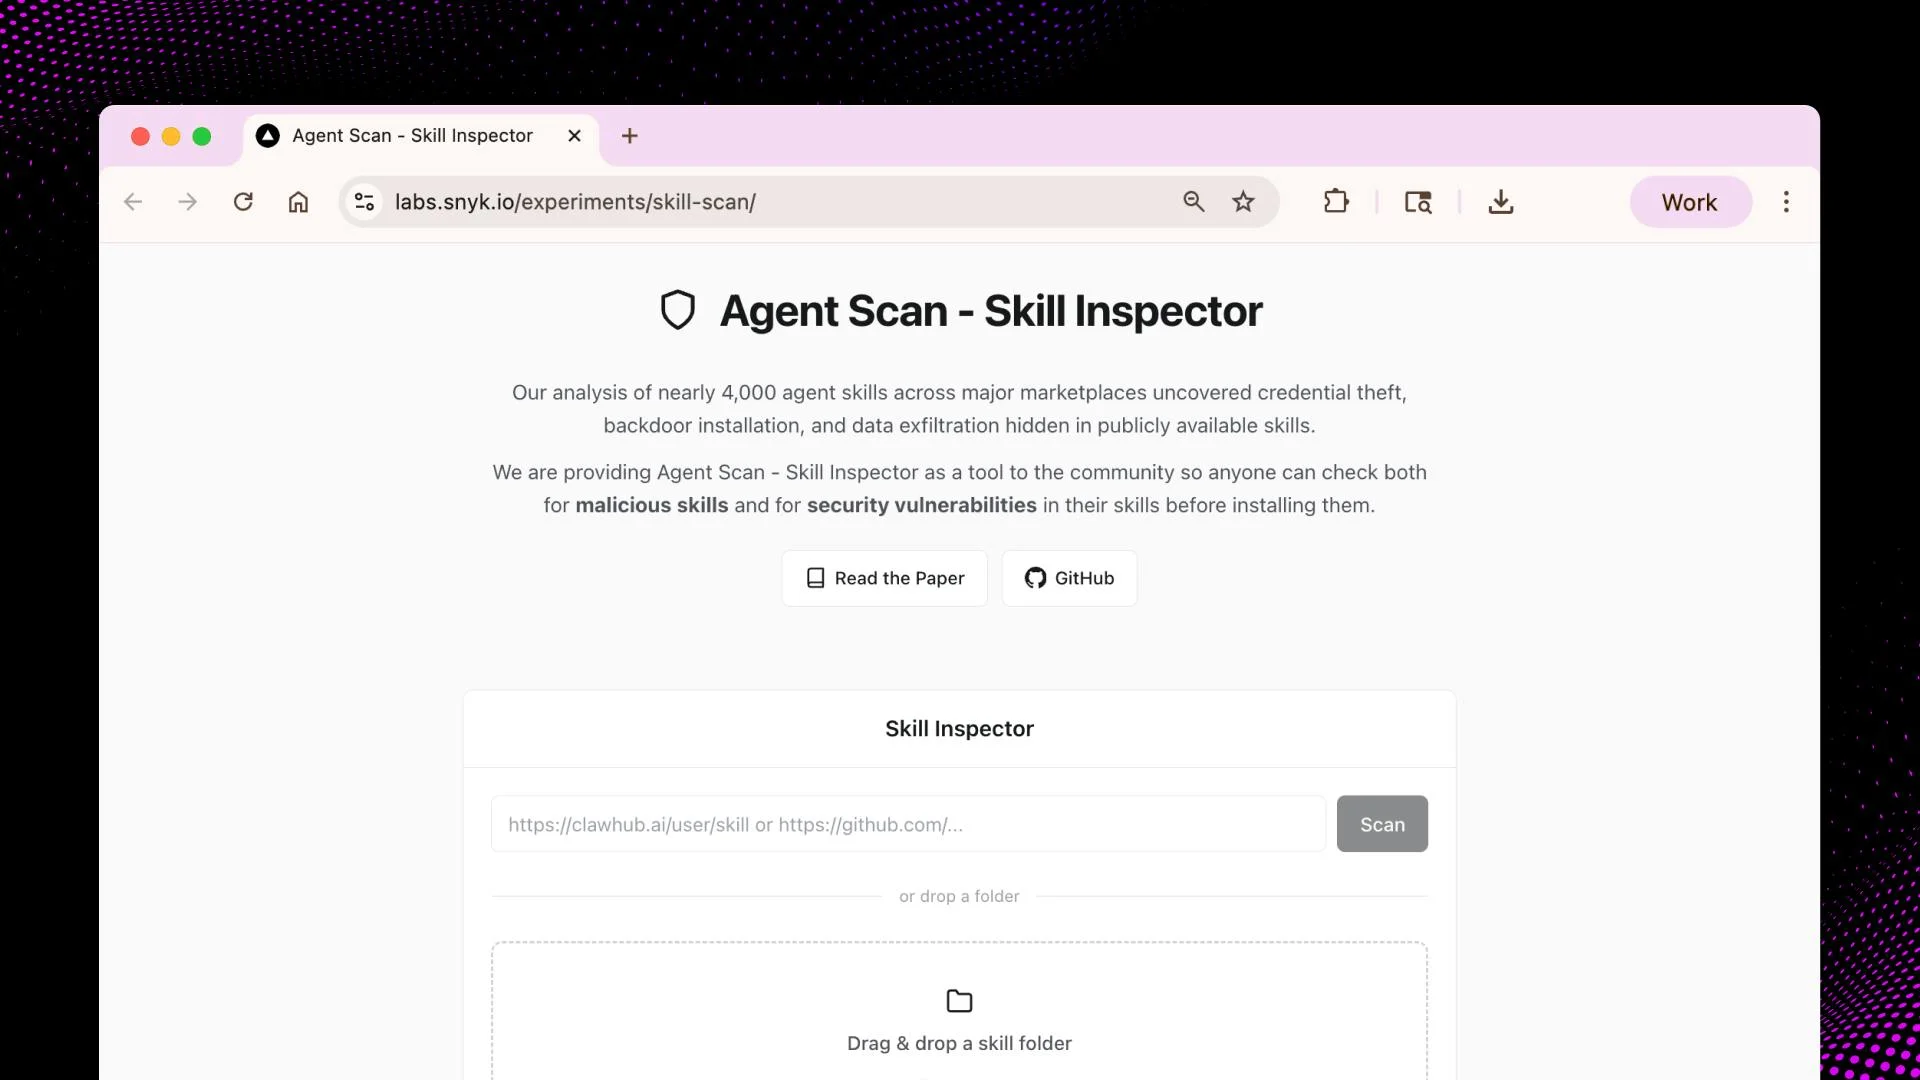
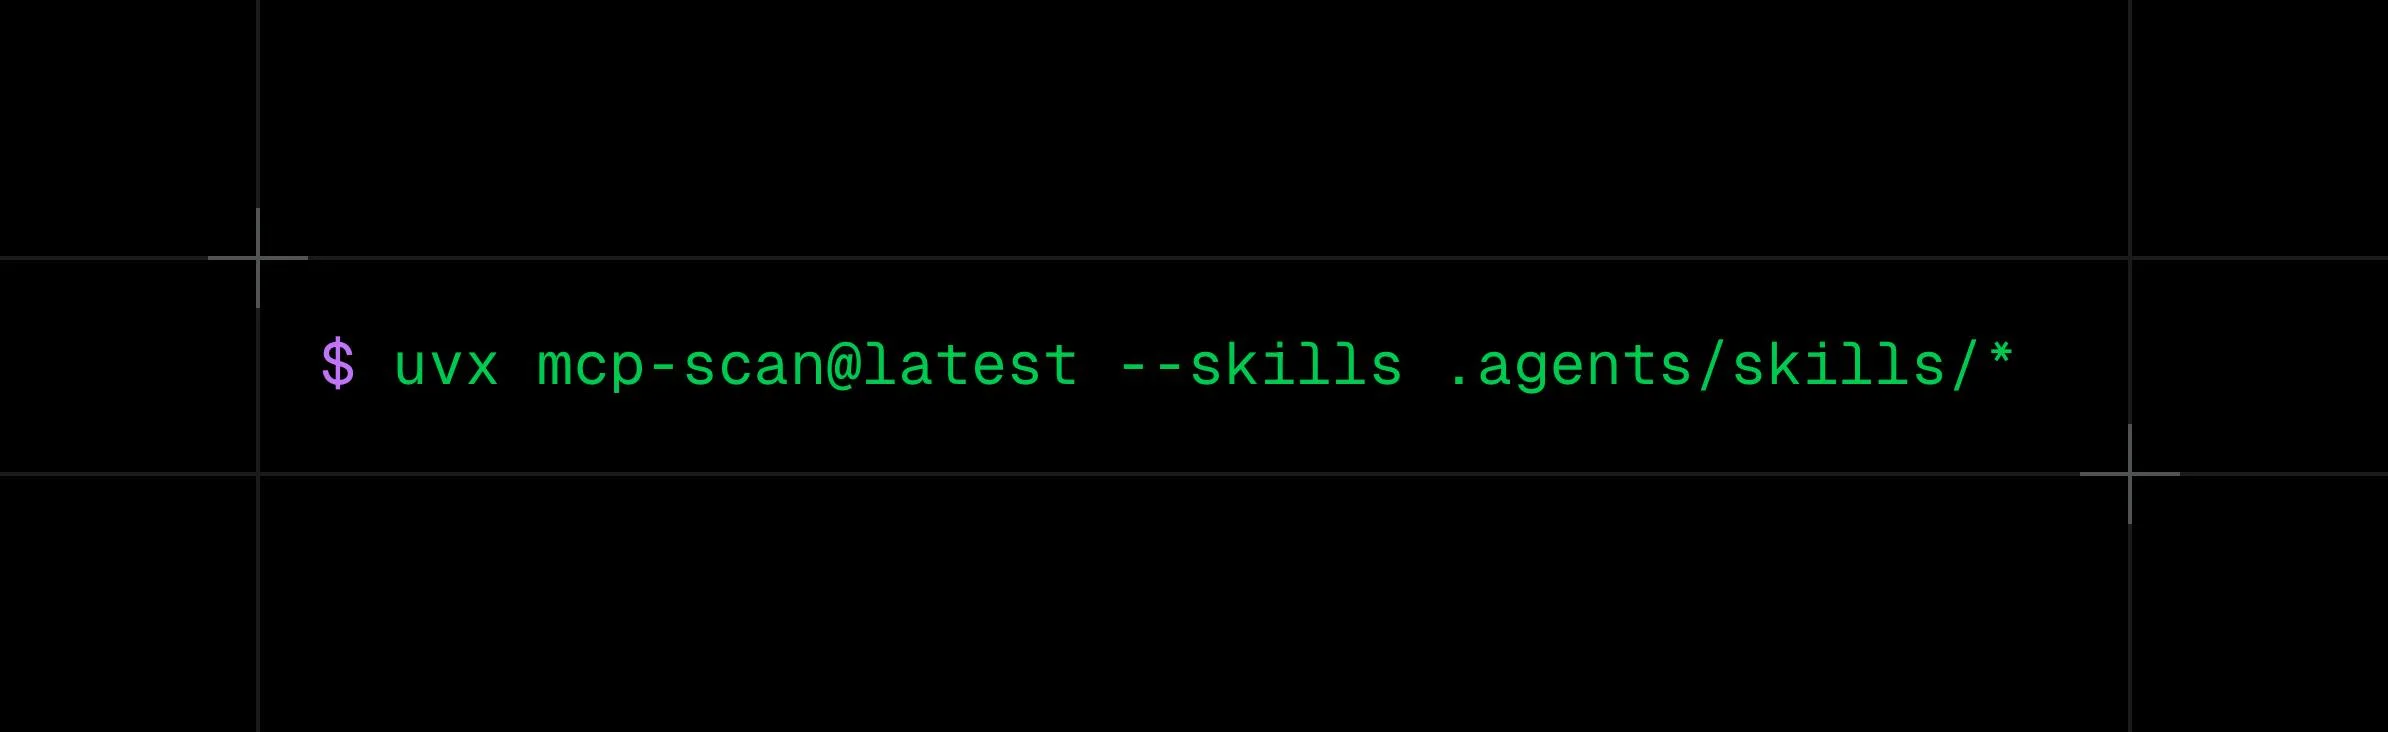
About Snyk
Snyk finds and fixes vulnerabilities while developers work, rather than after release. It scans first-party code, open source dependencies, containers and infrastructure files, and suggests or automates the fixes. It plugs into editors, repositories and CI pipelines so security checks run where the code already lives. Teams building with AI coding assistants also use it to catch risky generated code. A free plan is available, with paid tiers for larger organisations needing reporting and governance.
Reviews
From people who have used it. One review per person, checked by a human.
No reviews yet. Be the first to say something useful.